DevSecOps interview questions should test more than whether a candidate knows the names of security scanners. A strong answer connects software delivery, cloud security, CI/CD, identity, secrets, containers, Infrastructure as Code and incident response.
This guide covers practical questions that commonly reveal whether someone understands how security actually fits into DevOps workflows. The answers are intentionally concise enough for interview preparation but detailed enough to show the reasoning interviewers usually look for.
1. What Is DevSecOps?
DevSecOps means integrating security practices into software development and operations instead of treating security as a separate final gate. In practice, that can include threat modeling, secure coding, automated testing, dependency checks, secrets scanning, container scanning, policy enforcement, runtime monitoring and feedback from incidents.
NIST’s Secure Software Development Framework is designed to integrate secure-development practices into different SDLC models, while OWASP’s DevSecOps guidance focuses on embedding security activities into CI/CD pipelines.
2. What Does “Shift Left” Mean in DevSecOps?
Shift left means finding some security problems earlier in the software lifecycle, when they are usually cheaper and faster to fix. Examples include secrets scanning before code is merged, dependency scanning in CI, and Infrastructure-as-Code policy checks before deployment.
A strong answer should add that shift left does not mean “security only happens early.” Runtime monitoring, incident response, patching and production controls remain necessary.
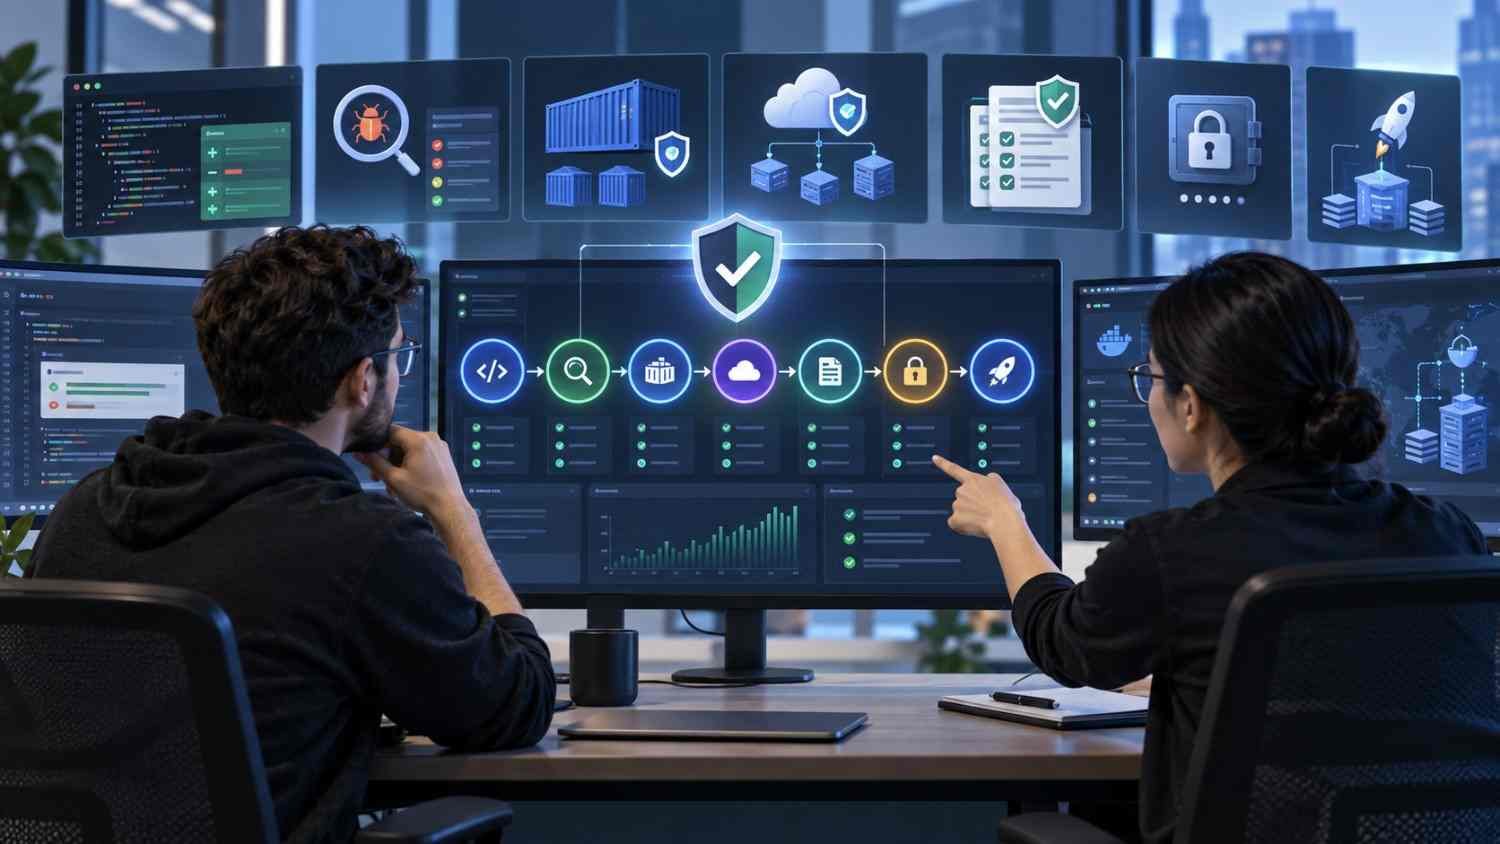
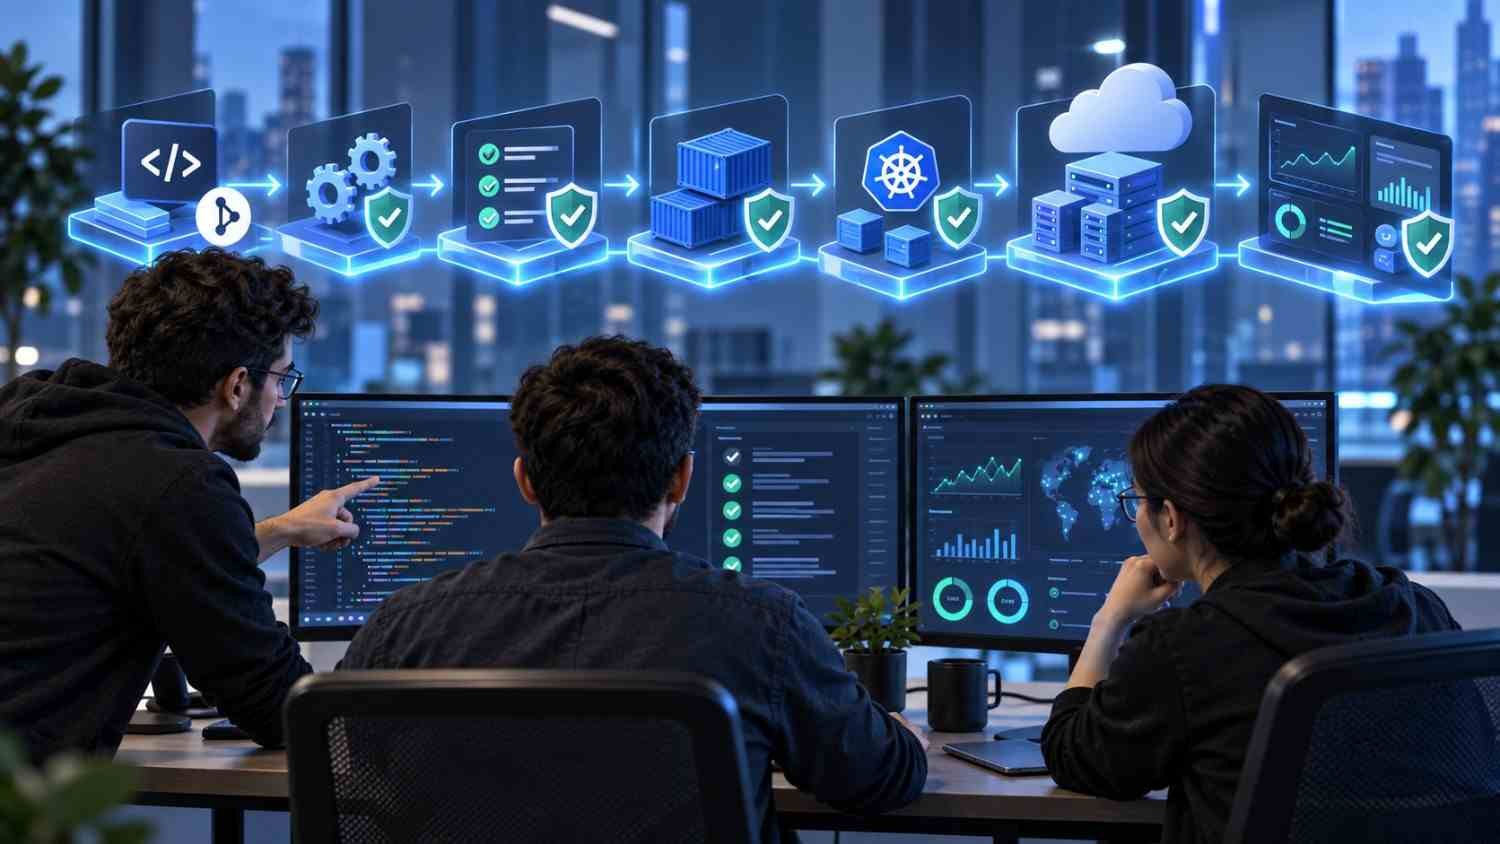
3. What Security Checks Would You Put in a CI/CD Pipeline?
- Secrets scanning
- Static application security testing (SAST)
- Software composition analysis (SCA) for vulnerable dependencies
- Container-image scanning
- Infrastructure-as-Code scanning
- License and policy checks where required
- Artifact signing or provenance generation
- Deployment-policy checks for sensitive environments
The right pipeline should prioritize meaningful controls rather than blocking every build on every scanner finding. Teams need severity thresholds, ownership, exception handling and a way to reduce false positives.
4. How Should Secrets Be Managed in CI/CD?
Secrets should not be hardcoded in repositories, Dockerfiles or pipeline YAML. Use the CI platform’s secret store or an external secrets manager, restrict who can access each secret, prefer short-lived credentials where possible, and rotate credentials immediately after suspected exposure.
Long-lived cloud keys are especially risky because exposed credentials can stay usable for years. See our analysis of leaked AWS keys and long-lived credential exposure.
5. What Is the Difference Between SAST, DAST and SCA?
| Control | What It Examines | Typical Use |
|---|---|---|
| SAST | Source code or compiled code | Find insecure coding patterns before deployment |
| DAST | Running application | Test externally observable application behavior |
| SCA | Third-party dependencies | Identify vulnerable or risky packages and licenses |
They complement each other. No single scanner provides complete application security coverage.
6. How Do You Secure Docker Images?
- Use trusted and minimal base images
- Pin versions where appropriate and rebuild regularly
- Run processes as a non-root user when possible
- Remove unnecessary packages and build tools from runtime images
- Scan images for known vulnerabilities
- Never bake credentials into image layers
- Sign or attest release artifacts where your supply-chain model requires it
7. How Do You Secure Kubernetes in a DevSecOps Workflow?
Start with least privilege and workload isolation: use RBAC carefully, dedicated service accounts, namespaces where they provide useful separation, network policies, resource limits, secure secret handling and admission policies. Scan images and manifests before deployment, but also monitor the cluster at runtime.
An interview answer is stronger when it mentions that Kubernetes security is layered: cloud IAM, cluster RBAC, workload identity, network controls, container security and application security all matter.
8. What Is Infrastructure-as-Code Security?
Infrastructure-as-Code security means reviewing and testing infrastructure configuration before it becomes production infrastructure. Common checks include public exposure, overly broad IAM, missing encryption, insecure security groups, unprotected storage and unsafe Kubernetes configuration.
It also includes protecting Terraform state and understanding drift. A scanner cannot solve every operational problem; teams still need a controlled workflow for reconciling manual changes. See our Terraform state drift guide.
9. How Would You Handle a Secret Accidentally Committed to Git?
- Revoke or rotate the secret immediately. Do not wait for repository-history cleanup.
- Investigate usage. Review cloud, application or identity logs for unauthorized activity.
- Remove the secret from the repository history if required for hygiene and future scanning.
- Fix the process: add secret scanning, improve credential storage and reduce use of long-lived credentials.
The key interview point is that deleting the Git commit does not make an exposed credential trustworthy again.
10. What Is Least Privilege?
Least privilege means giving a user, workload or service only the permissions it needs for the required task, and no broader access than necessary. In cloud environments this often means scoping actions, resources, conditions and session duration rather than attaching broad administrator policies.
11. What Is the Difference Between Authentication and Authorization?
Authentication answers who are you? Authorization answers what are you allowed to do? DevSecOps engineers need both because a correctly authenticated user can still be overprivileged.
This distinction is especially important for AI agents and automated workloads. Our AWS Bedrock AgentCore security guide shows how user context and downstream authorization can limit what an agent is allowed to access.
12. How Do You Prioritize Vulnerabilities?
Do not prioritize only by CVSS. Combine severity with exploitability, internet exposure, asset value, privilege requirements, available mitigations, evidence of active exploitation and the potential business impact.
For example, an actively exploited vulnerability on an internet-facing GitLab server may deserve faster action than a higher-scoring issue that is unreachable in your environment. Our coverage of GitLab CVE-2026-85706 illustrates why exploitation evidence changes response priority.
13. What Is Software Supply-Chain Security?
Software supply-chain security protects the path from source code to the artifact users receive. It includes source control, dependencies, build systems, CI/CD identities, package registries, provenance and release integrity.
SLSA provides a framework for increasing confidence in build provenance and build-system integrity. Higher SLSA build levels add stronger guarantees around provenance and hardened build infrastructure.
14. What Is SBOM and Why Is It Useful?
A Software Bill of Materials (SBOM) is an inventory of software components and dependencies. It can help teams answer questions such as “Do we use this vulnerable library?” or “Which applications contain this package?” It improves visibility, but an SBOM by itself does not fix vulnerabilities or prove that a build is trustworthy.
15. How Do You Reduce False Positives from Security Scanners?
Start by tuning rules for the technology stack, defining severity and confidence thresholds, suppressing findings only with documented justification, assigning ownership and reviewing recurring exceptions. Security automation should improve signal, not train developers to ignore every pipeline warning.
16. What Is a Security Gate in CI/CD?
A security gate is a rule that decides whether a build or deployment can continue. Examples include blocking a release when a critical exploitable dependency is present, when secrets are detected, or when a production IaC change violates a mandatory policy.
Not every finding should be a hard gate. Good pipelines differentiate between blocking conditions, warnings and accepted risk.
17. How Would You Secure a GitHub Actions or GitLab CI Pipeline?
- Use least-privilege pipeline permissions
- Protect production branches and environments
- Pin or review third-party actions and reusable pipeline components
- Prefer short-lived cloud federation over static access keys
- Limit secret exposure to only the jobs that require it
- Require approvals for sensitive production actions where appropriate
- Keep runners patched and isolate high-risk or untrusted workloads
18. What Would You Monitor After Deployment?
Monitor authentication events, authorization failures, privileged API activity, deployment changes, unusual network behavior, application errors, security alerts and access to sensitive data. DevSecOps does not end when the deployment succeeds.
19. How Do NIST SSDF and DevSecOps Relate?
NIST SSDF provides a set of high-level secure software-development practices that organizations can integrate into their existing SDLC. NIST’s 2026 DevSecOps work demonstrates how SSDF practices can be implemented using modern DevSecOps pipelines and tooling.
20. What Is the Best Way to Answer DevSecOps Scenario Questions?
Use a simple structure: identify the immediate risk, contain it, preserve evidence, fix the vulnerable control, verify recovery and then improve the process so the same issue is less likely to recur.
For example, if an interviewer says, “A production AWS key was exposed in GitHub,” do not start with repository cleanup. Start with revocation, log review and impact analysis. That demonstrates operational security judgment rather than tool memorization.
Rapid-Fire DevSecOps Interview Questions
- What is the difference between a vulnerability and a risk?
- Why are short-lived credentials safer than long-lived keys?
- When would you block a pipeline?
- How do you scan Infrastructure as Code?
- What is admission control in Kubernetes?
- What is artifact provenance?
- What is dependency confusion?
- What is a secrets manager?
- Why should production runners be isolated?
- How would you respond to a critical zero-day when no patch exists?
DevSecOps Interview Preparation Checklist
- Be able to explain one CI/CD pipeline you built or supported.
- Prepare one incident or failure example and explain your response.
- Know IAM, secrets, Docker, Kubernetes and IaC security basics.
- Understand SAST, DAST, SCA and container scanning.
- Know why short-lived credentials and least privilege matter.
- Practice scenario answers instead of memorizing definitions only.
Bottom Line
The best DevSecOps interview questions test whether you can apply security controls without breaking delivery. Strong candidates understand the trade-offs between automation, developer experience, cloud permissions, supply-chain integrity and incident response—and can explain how they would respond when a control fails.
